The marketing geniuses finally hit the sweet spot by realizing that every guy likes stuff that blows up.
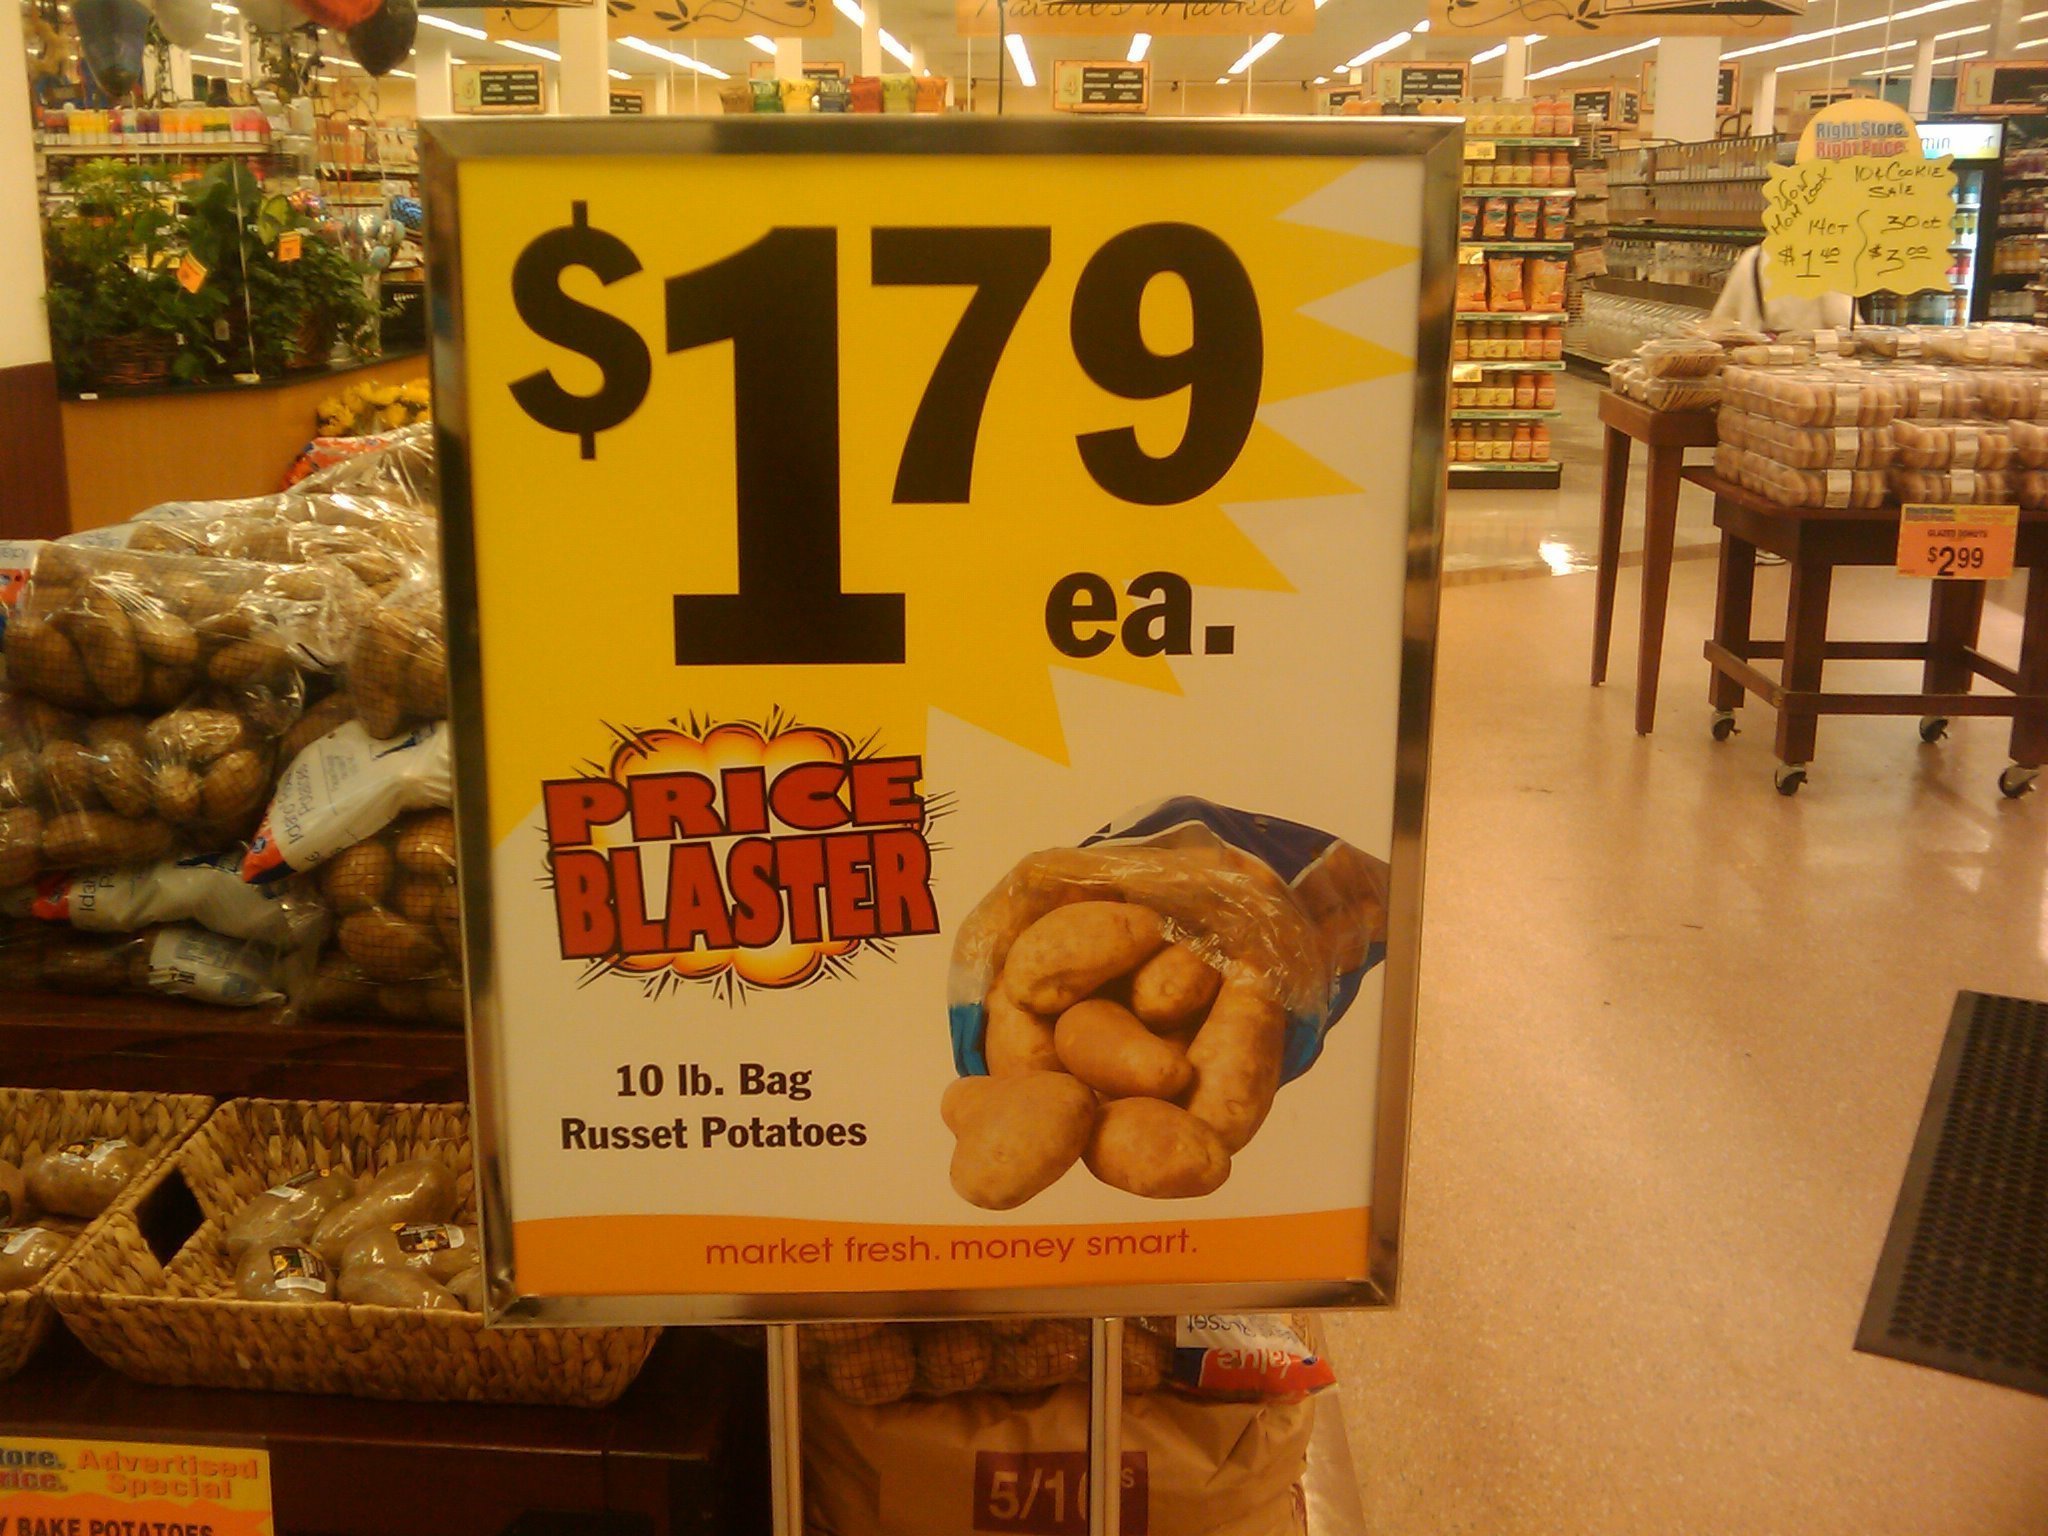
In the U.S. of A they don’t just reduce, decrease or even cut prices. They blast them! Fuck yeah! Give me 10 bags of that shit!
The marketing geniuses finally hit the sweet spot by realizing that every guy likes stuff that blows up.
In the U.S. of A they don’t just reduce, decrease or even cut prices. They blast them! Fuck yeah! Give me 10 bags of that shit!
This assumes that you have postfix installed and running as your SMTP server
First, make sure that you’re root
[bash]whoami[/bash]
I probably shouldn’t have to explain that if you’re reading this but just in case; if that last command returned something else than ‘root’ issue the following command
[bash]sudo su[/bash]
and enter your password
[bash]apt-get update
apt-get install spamassassin spamc[/bash]
step 2: Now we configure spamassasin
[bash]cat /etc/default/spamassassin | sed -e ‘s#ENABLED=0#ENABLED=1#g’ > /etc/default/spamassassin
cat /etc/default/spamassassin | sed -e ‘s#CRON=0#CRON=1#g’ > /etc/default/spamassassin
cat /etc/spamassassin/local.cf | set -e ‘s## rewrite_header Subject *****SPAM*****#rewrite_header Subject [*****SPAM*****] > /etc/spamassassin/local.cf[/bash]
and we start/restart it
[bash]/etc/init.d/spamassassin restart[/bash]
create a user called spamassassin (or whatever you want as long as you keep it consistent)
[bash]useradd -m spamassassin[/bash]
then edit the script file /home/spamassassin/spamcheck and throw the following in it
[bash] # variables
SENDMAIL="/usr/sbin/sendmail -i"
EGREP=/bin/egrep
SPAMLIMIT=10
# exit codes from <sysexits.h>
EX_UNAVAILABLE=69
# clean up when done or when aborting.
trap "rm -f /tmp/out.$$" 0 1 2 3 15
# pipe message to spamc
cat | /usr/bin/spamc -u spamd > /tmp/out.$$
# are there more than $SPAMLIMIT stars in X-Spam-Level header? :
if $EGREP -q "^X-Spam-Level: *{$SPAMLIMIT,}" < /tmp/out.$$
then
# option 1: move spam messages to sideline dir so a human can look at them later:
mv /tmp/out.$$ /home/spamassassin/`date +%Y-%m-%d_%R`-$$
# option 2: divert spam message to an alternate e-mail address:
#$SENDMAIL xyz@xxxx.xx < /tmp/out.$$
# option 3: just delete the spam message
# rm -f /tmp/out.$$
# option 4: still relay the email to the recipient with the subject of the email now containing [*****SPAM*****]
# $SENDMAIL "$@" < /tmp/out.$$
else
$SENDMAIL "$@" < /tmp/out.$$
fi
# Postfix returns the exit status of the Postfix sendmail command.
exit $?[/bash]
make sure that you
[bash]chown spamassassin:spamassassin /home/spamassassin/spamcheck
chmod 750 /home/spamassassin/spamcheck[/bash]
edit /etc/postfix/master.cf and replace
[code]smtp inet n – – – – smtpd[/code]
with
[code]smtp inet n – n – – smtpd -o content_filter=spamcheck:dummy[/code]
also add the following 2 lines at the bottom of the file (the indentation is important)
[code]spamcheck unix – n n – 10 pipe
flags=Rq user=spamassassin argv=/bin/spamcheck -f ${sender} — ${recipient}[/code]
We’re almost there, just restart postfix and you’re good to go!
[bash]/etc/init.d/postfix restart[/bash]
If you wanna test that out, watch the log while you send emails to your servers
[bash]tail -f /var/log/syslog[/bash]
send a clean mail, make sure that it reaches destination, then send something you know will get flagged as spam and make sure it ends up in /home/spamassasin instead of the intended recipient.
The reason we choose option 1 here is because there’s no point in still relaying a flagged email as it will still clog the recipient’s mailbox. On the other hand we don’t want to just delete it if spamassassin makes a mistake we want to play it safe and keep every emails should something arise, we quarantine the bad ones in /home/spamassassin
Lastly, as long as you have postfix just feeding the emails to a script like we just did, it’s easy to become fancier and do all kinds of processing to the email, on my server I actually call a php script that throws emails in a DB.
If the following happens to you:
[code]apache2: Could not reliably determine the server’s fully qualified domain name, using 127.0.1.1 for ServerName[/code]
just issue a:
[bash]echo Servername `cat /etc/hostname` >> /etc/apache2/apache2.conf[/bash]
Tested on: Ubuntu server 9.04 32b / Ubuntu 12.04 64b
Sad balloons are sad
Proud balloon reporting for duty!
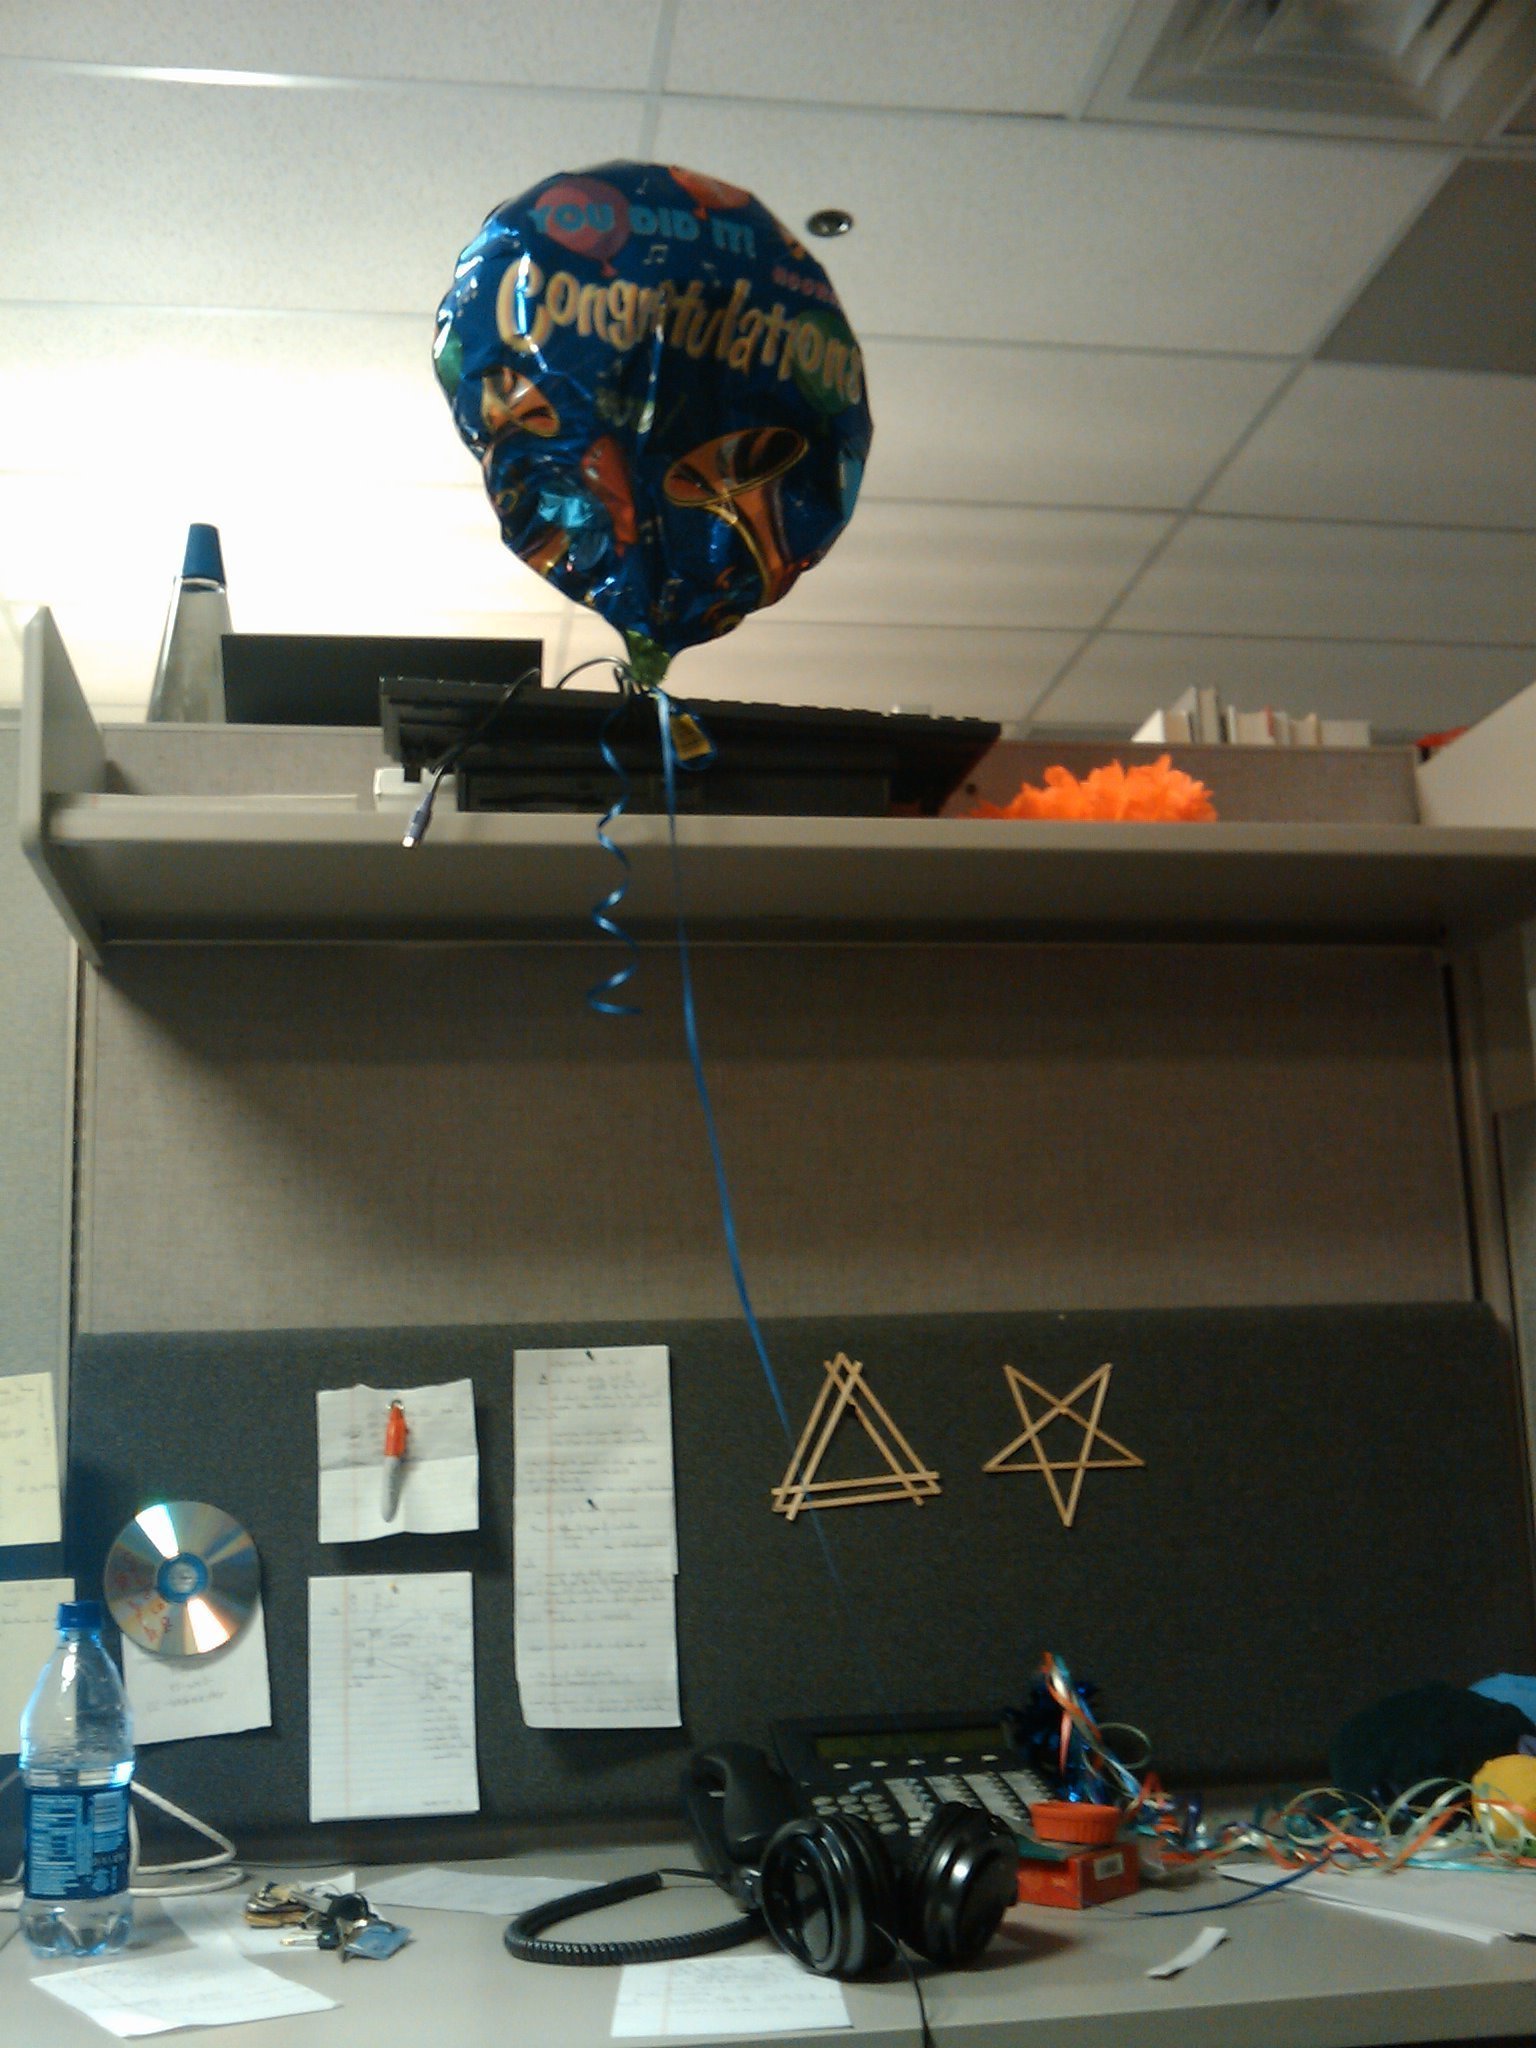
A month after being saved from the corporate world, this is what’s left of the welcome balloons that were kindly positioned at my new desk.
This little guy’s been floating for 38 days. When it finally gives in I’m giving it a Viking funeral.
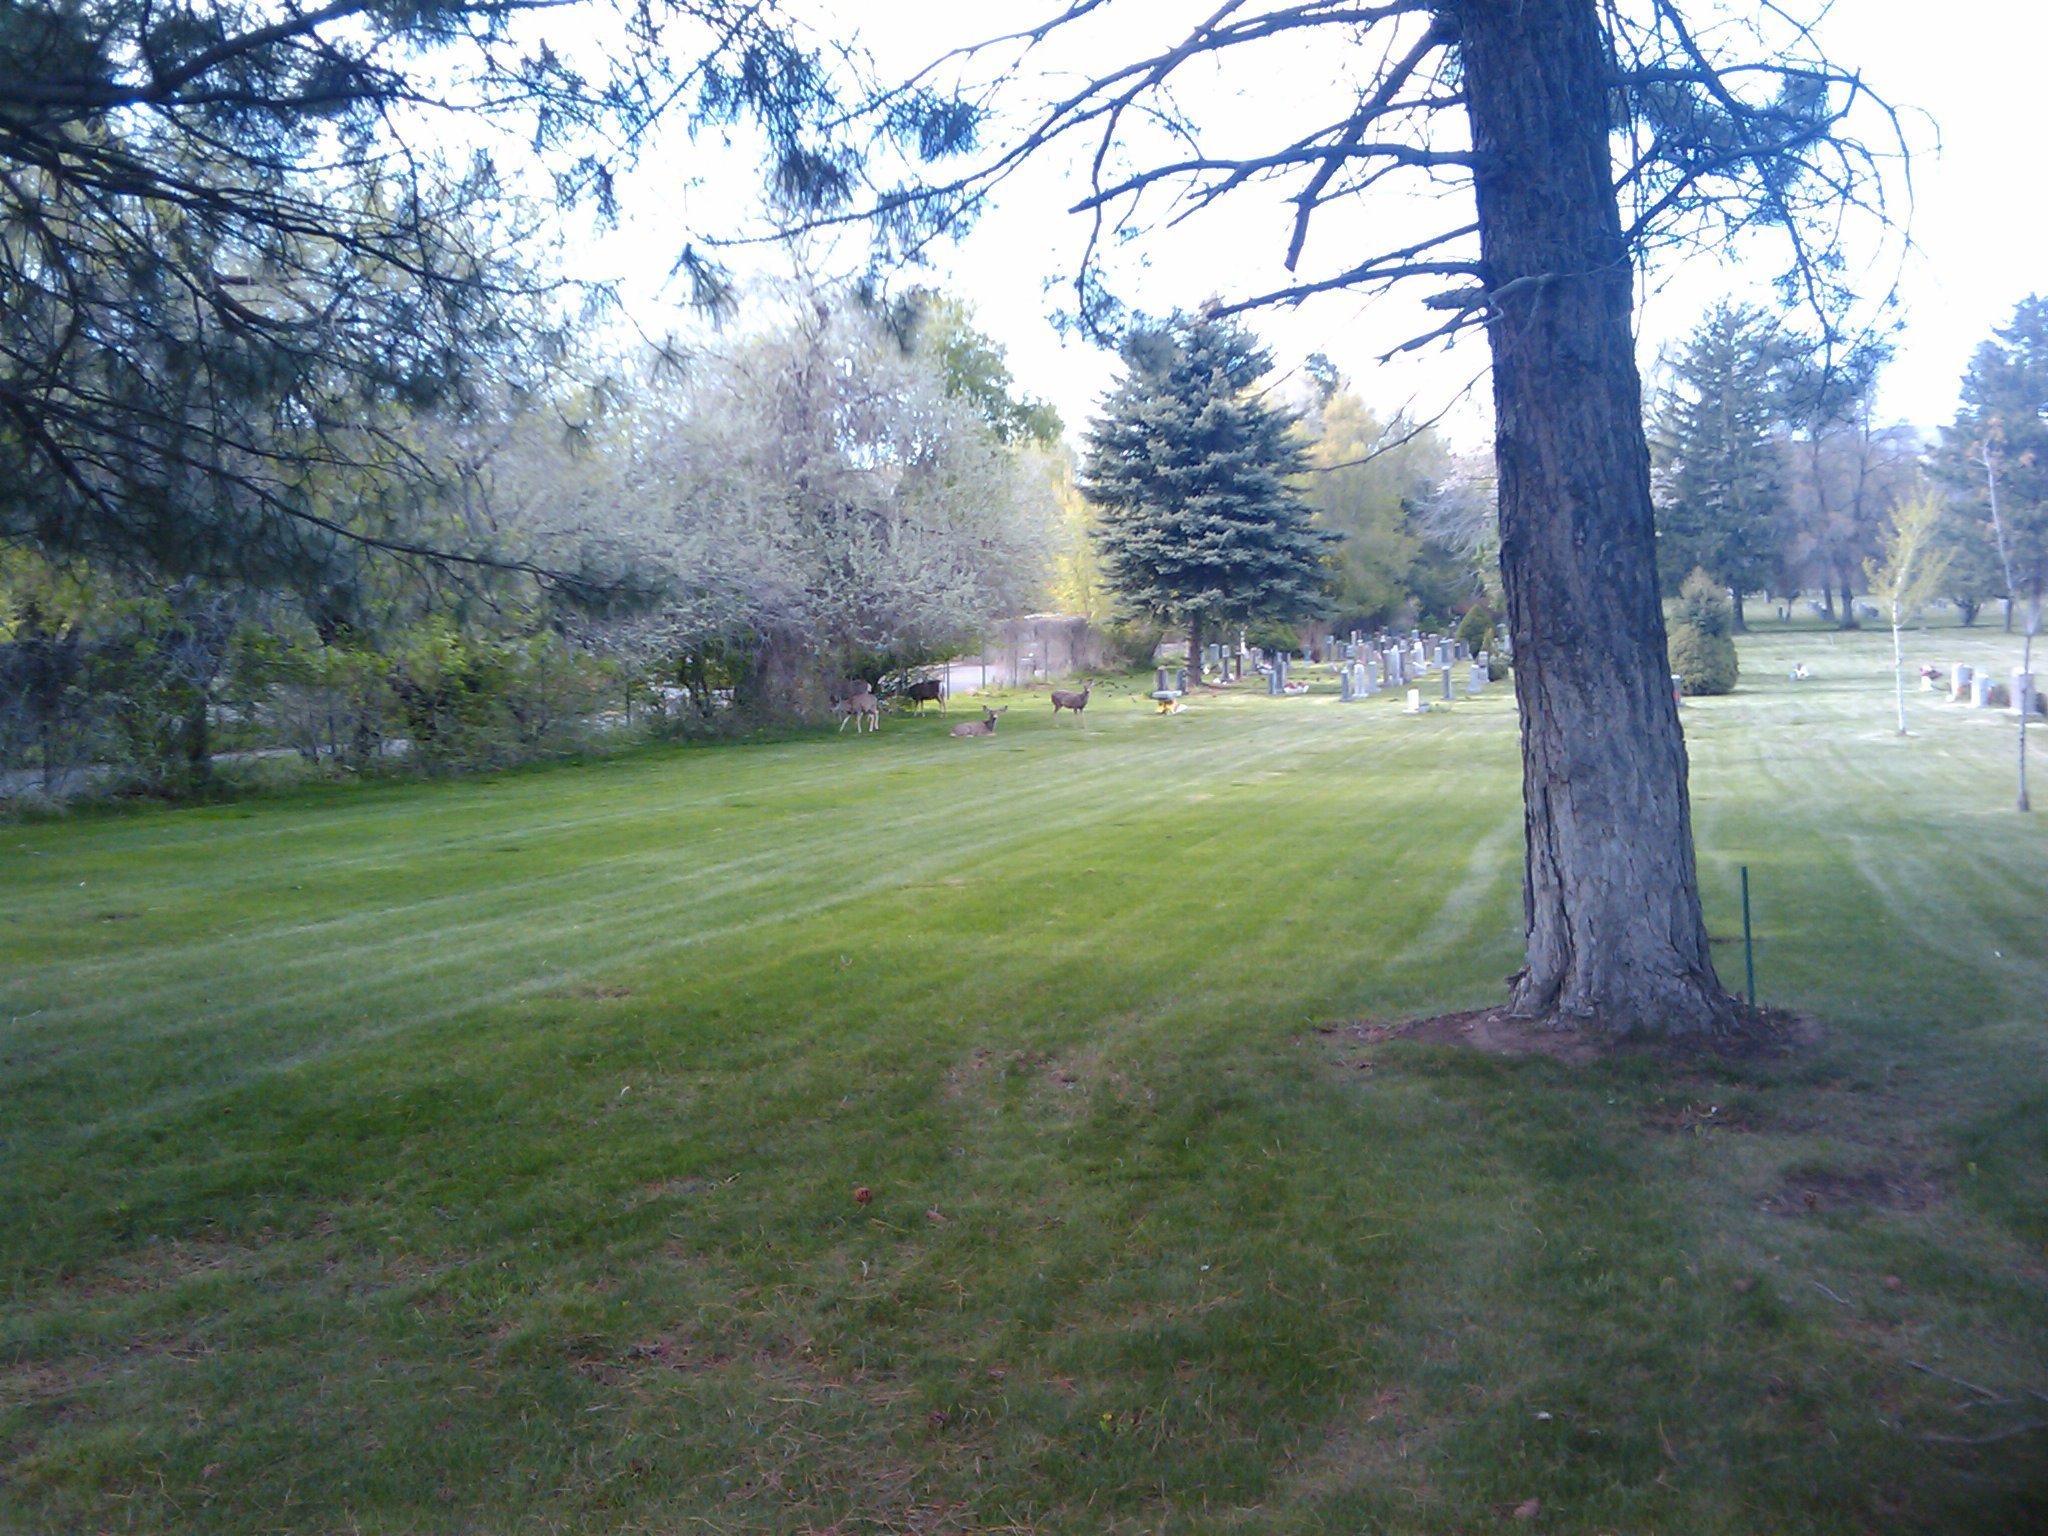
It’s not rare to see a deer wandering around in Salt Lake City. The other day, I rode through a vast cemetary that’s tightly surrounded by a fence (I know how tight it is cause I was trying to find a shortcut through the cemetery and pretty much had to exit where I came in). In 2 minutes I saw 9 deers hanging around.
I’m not sure how they got there and if they’ll ever leave,
here’s 5 of them enjoying a quiet afternoon:

And 4 more:
Il n’est pas rare qu’au milieu du courrier, parmis les offres de cartes de credit, se cache une relance pour acheter des bibelots. Jusqu’ici pas de quoi en faire un plat. Seulement les objects en question sont d’un mauvais gout a en faire palir le cul d’un Anglais. Nicole et moi les avons garde religieusement au cours de ces derniers annees. Ont les regarde un peu comme un album photo de temps a autres pour se marrer un coup.
Sans plus tarder voici la collection:
We’re gonna start easy with the most discusting idea a marketing genius ever had, I give you:
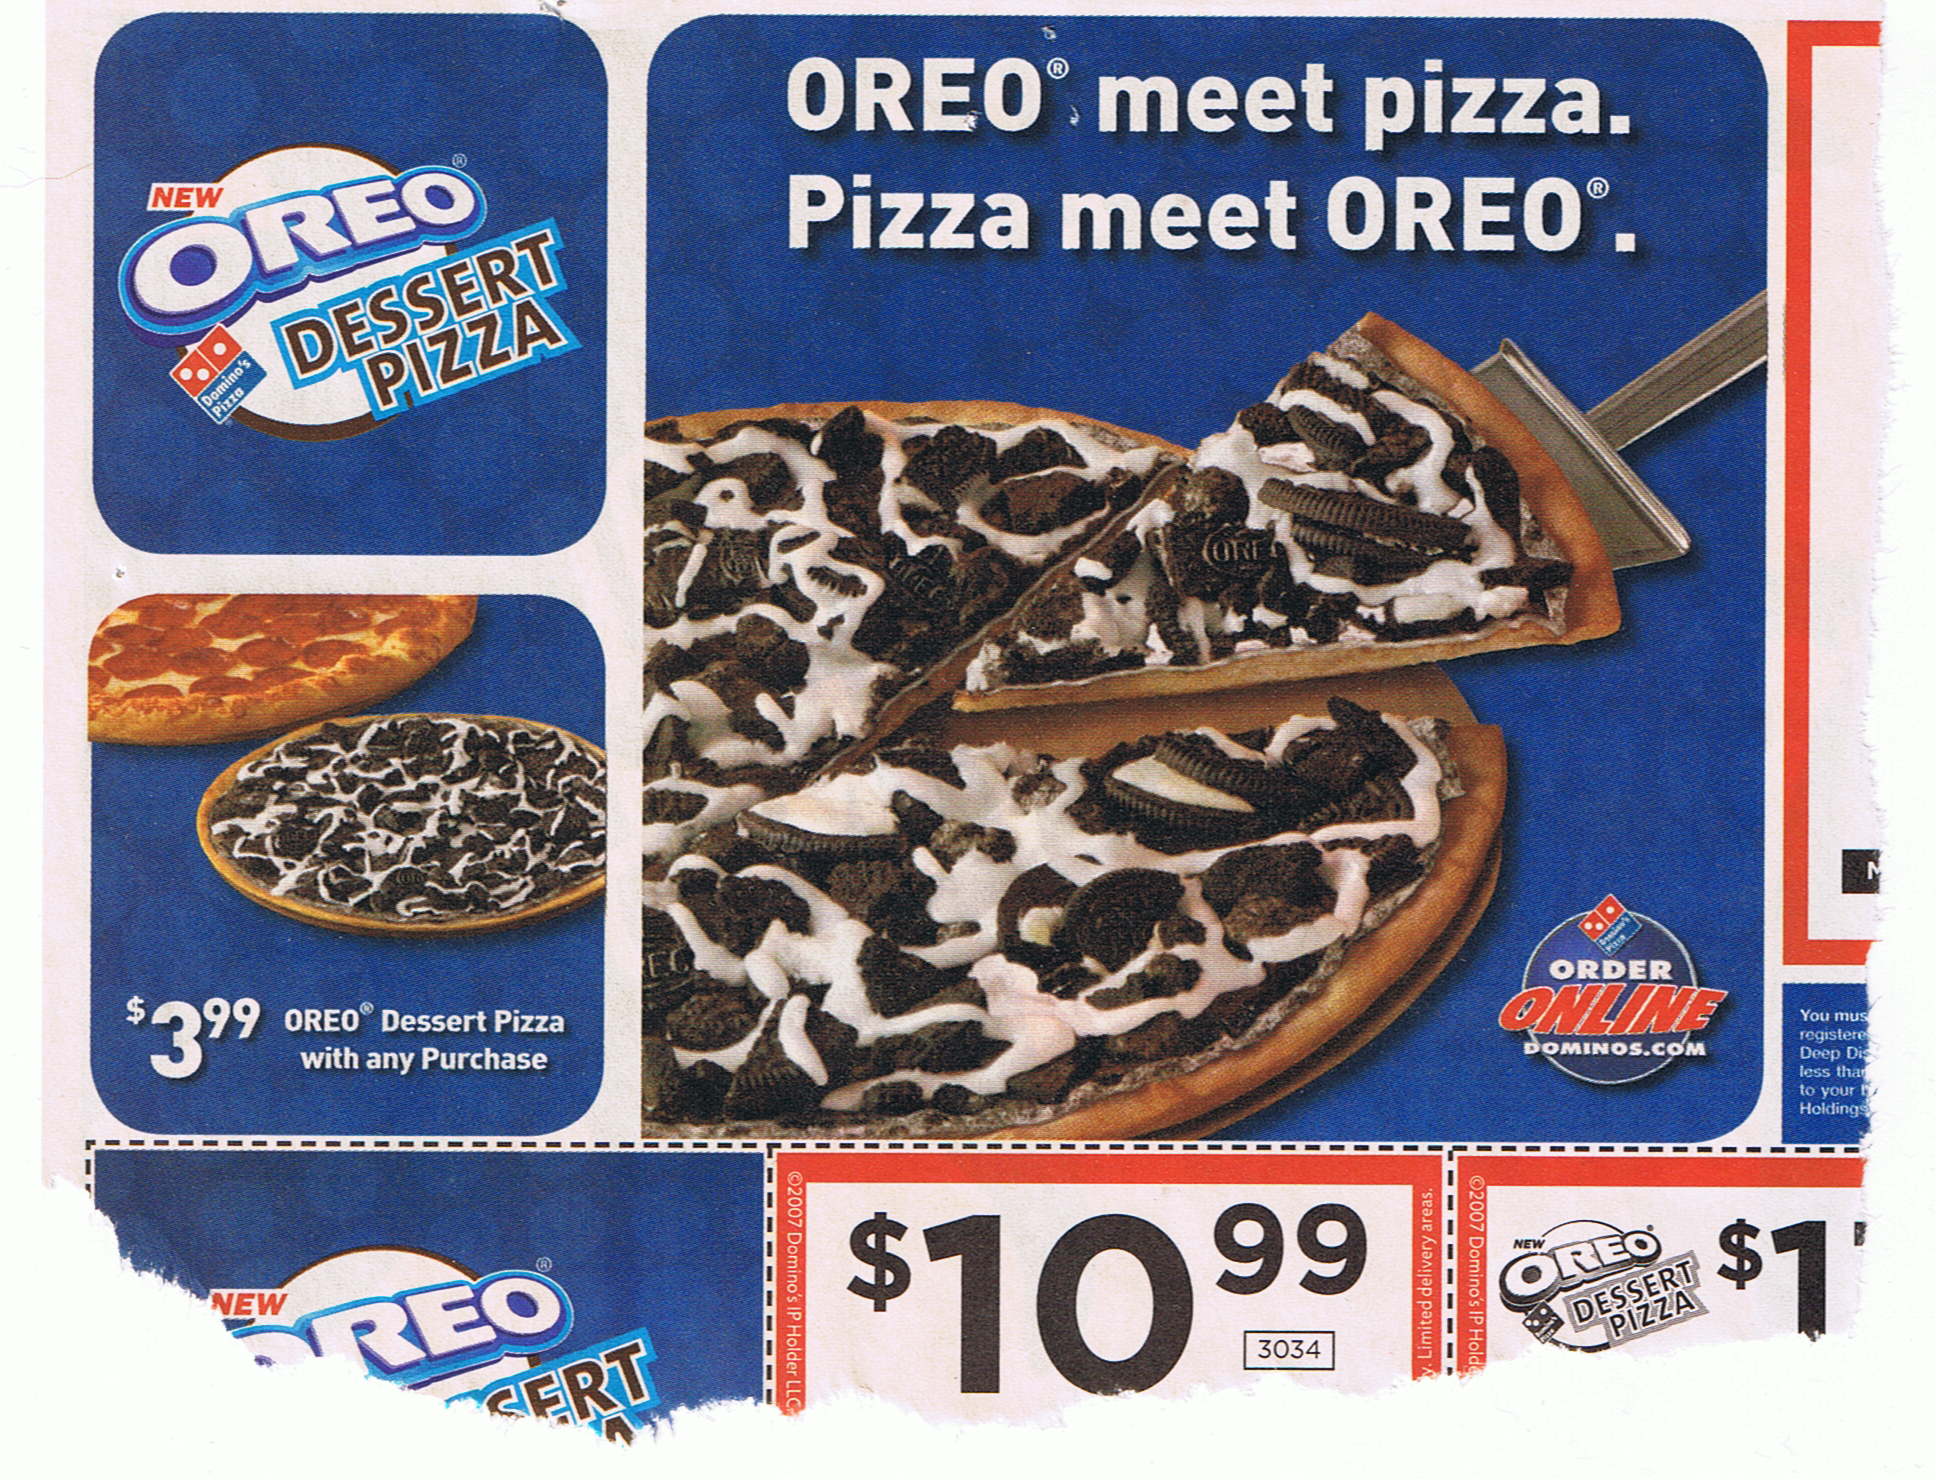
Last time I bought a pizza from Domino’s, they threw free cinamon sticks with it. Rather than be filled with the smell of delicious pizza, my car stunk cinamon like it’s Christmas at the gay ass mall.
Domino’s, inventing puke inducing recipes since 1960
Here’s a neat little command that will let you delete specified files/directories recursively and based on their names.
Let’s do a dry run first to make sure that the command will go through the right files. Run:
[bash]<code class="plain plain">find <directory_to_start_the_recursion_in> -name <file_name</code>>[/bash]
Keep in mind that if you’re gonna have asterisks (*) in the <file_name> you need to escape them like so:
[bash]find /var/www -name *.jpg[/bash]
make sure that the result only lists the files/directories that you indeed want to obliterate. Then improve that last command by adding:
[bash]find <directory_to_start_the_recursion_in> -name <file_name> -exec rm -rf {} ;[/bash]
Since this is a pretty dangerous command even after a dry run, you can use -ok instead of -exec which will prompt you for approval everytime the command it executed.
[bash]find <directory_to_start_the_recursion_in> -name <file_name> -ok rm -rf {} ;[/bash]
This is of course not limited to rm 🙂
Left4Dead is far from obsolete but lately I grew a little sick of playing the same maps over and over. The special zombies too are getting kinda old. This is when I came accross Killing Floor. Very little information is currently available about it on the web, a couple of videos on youtube and the official game site.
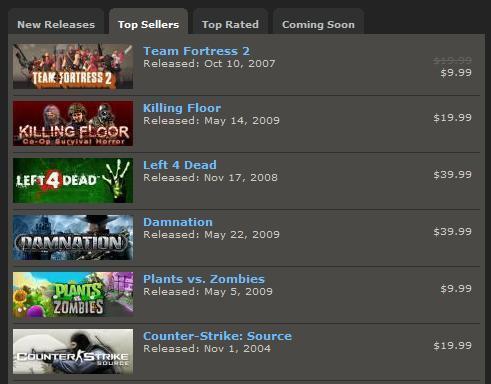
It’s currently one of the most sold game on Steam showing the strong liking that people are taking with coop massacring of zombies.
Let’s go straight to the point: the games needs to be polished the fuck out. It’s very bulky, buggy & glitchy but it is built right. The game obviously got released too early and while it seems like the people in charge are proactive about fixing all of that, one can only hope that they’ll keep doing so until they have an acceptable product.
The gameplay is just weird, moving around doesn’t feel right.
The maps aren’t the best but they’re good enough.
The monsters you get to kill are pretty cool.
Graphics aren’t bad at all.
The AI’s not the best too and so repetitiveness becomes an issue early.
The music is really good.
Sound effects on the other hand are awkward.
but really this all needs to be patched like there’s no tomorrow.
I threw a quick video together since as I said earlier, only very little info can currently be found about this game:
It’s for sale for $20 on Steam, I’ve played for about 2 hours and don’t have much more in me. Not really worth it unless you don’t mind throwing money out the window. There used to be a time where games were released as finished products…
Here’s a cool little script that will recursively chmod, giving a permission based on whether it’s dealing with a file or a directory. This is very convenient when you want to add that +x to directories but not files.
[bash]find $1 -type f -exec chmod $2 {} ;
find $1 -type d -exec chmod $3 {} ;[/bash]
Go ahead and edit /usr/bin/chmod_script, copy paste these 2 lines in there, then issue a chmod 755 /usr/bin/chmod_script as root, that’s it!
Usage syntax is as follows:
[bash]chmod_script <directory_to_start_the_recursion_in> <permissions_for_files> <permissions_for+directories>[/bash]
so if I want to use it on /var/www do:
[code]chmod_script /var/www 644 755[/code]
Enjoy!
Ca fait un bail que je vois passer le phenomene des blogs sans m’y interesser. Avec le changement complet d’Akrin je crois qu’il est temps de se mouiller les pieds. A moi le social networking, le web 2.0, et tout le tralala! Je vais vous podcaster la blogosphere comme si il n’y avait pas de lendemain.
Ca risque d’etre assez geeky faudra pas s’inquieter.
De quoi on va parler?
That’s all folks